Description
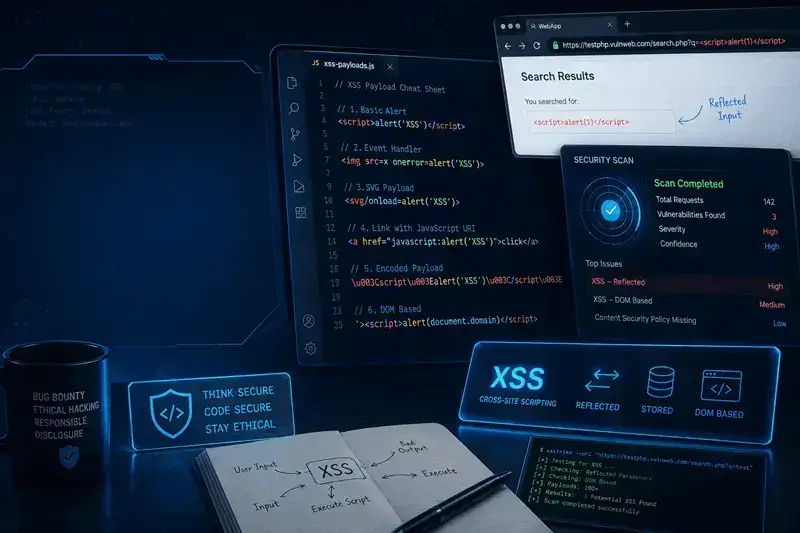
User-controllable URLs refer to HTML attributes with a value type of URI, such as href in the a tag or src in the img tag. When an application directly incorporates user input into these attributes, it allows malicious users to manipulate the browser behavior. This can result in XSS or Phishing attacks, where attackers exploit the manipulated URLs to execute scripts or deceive users.
Recommendation
To mitigate risks associated with user-controllable URLs, avoid directly incorporating user input as URIs in HTML attributes. Implement server-side validation and sanitization of user-supplied URLs to ensure they adhere to expected patterns and do not pose security risks.
References
Related Issues
- @samanhappy/mcphub: SSE Endpoint Accepts Arbitrary Username from URL Path Without Authentication, Enabling User Imperson - Vulnerability
- obsidian-local-rest-api: Authenticated path traversal via URL-encoded %2F in /vault/{path} — arbitrary host file read/wr - Vulnerability
- Authorization Bypass Through User-Controlled Key in url-parse - CVE-2022-0686
- React Native Sms User Consent Intent Redirection Vulnerability - CVE-2021-4438
You might also like:
- Tags:
- Phishing
- Cross Site Scripting (XSS)
- Input Validation
Anything's wrong? Let us know Last updated on May 13, 2024