Description
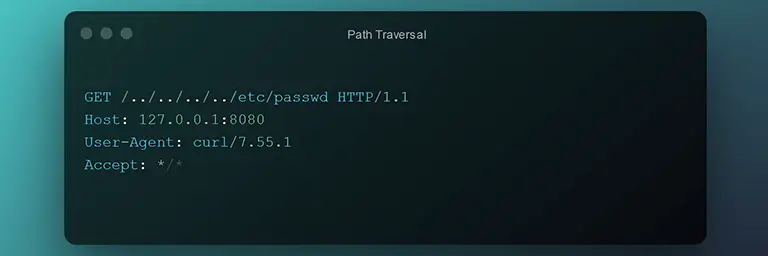
Path traversal in npm package rollup-plugin-serve before version 1.0.2. There is no path sanitization in readFile operation.
Recommendation
Update the rollup-plugin-serve package to the latest compatible version. Followings are version details:
- Affected version(s): < 1.0.2
- Patched version(s): 1.0.2
References
Could your website be exposed too?
SmartScanner can check your website for Path traversal in rollup-plugin-serve and gives you actionable findings to investigate.
Start a free scanRelated Issues
- MJML vulnerable to path traversal - CVE-2020-12827
- Path traversal vulnerability in gatsby-plugin-sharp - CVE-2023-30548
- Path Traversal in socket.io-file - CVE-2020-15779
- Rollup 4 has Arbitrary File Write via Path Traversal - CVE-2026-27606
You might also like:


See something that needs correcting? Let us knowUpdated February 01, 2023