Description
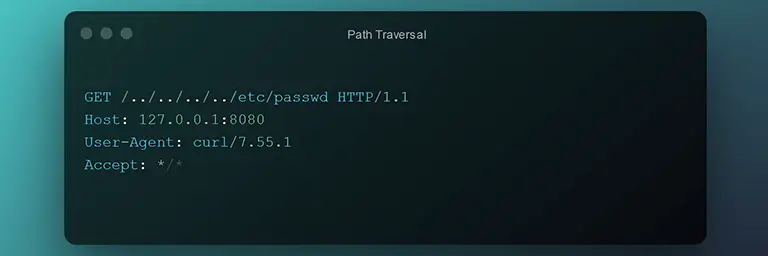
nanotar through 0.2.0 has a path traversal vulnerability in parseTar() and parseTarGzip() that allows remote attackers to write arbitrary files outside the intended extraction directory via a crafted tar archive containing path traversal sequence.
Recommendation
No fix is available yet. Followings are affected versions:
- <= 0.2.0
References
Could your website be exposed too?
SmartScanner can check your website for nanotar is vulnerable to path traversal in parseTar() and parseTarGzip() and gives you actionable findings to investigate.
Start a free scanRelated Issues
- Mammoth is vulnerable to Directory Traversal - CVE-2025-11849
- fast-uri vulnerable to path traversal via percent-encoded dot segments - CVE-2026-6321
- `@backstage/backend-common` vulnerable to path traversal through symlinks - CVE-2024-26150
- Agnai vulnerable to Relative Path Traversal in Image Upload - CVE-2024-47171
You might also like:

See something that needs correcting? Let us knowUpdated February 11, 2026