Description
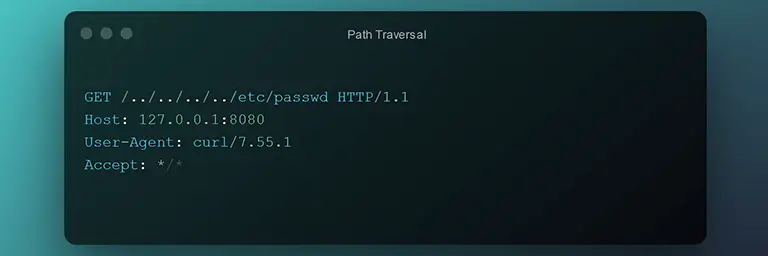
matrix-js-sdk before 34.11.0 is vulnerable to client-side path traversal via crafted MXC URIs. A malicious room member can trigger clients based on the matrix-js-sdk to issue arbitrary authenticated GET requests to the client’s homeserver.
Recommendation
Update the matrix-js-sdk package to the latest compatible version. Followings are version details:
- Affected version(s): < 34.11.1
- Patched version(s): 34.11.1
References
Could your website be exposed too?
SmartScanner can check your website for matrix-js-sdk has insufficient MXC URI validation which allows client-side path traversal and gives you actionable findings to investigate.
Start a free scanRelated Issues
- matrix-js-sdk has insufficient validation when considering a room to be upgraded by another - CVE-2025-59160
- Matrix JavaScript SDK's key history sharing could share keys to malicious devices - CVE-2024-47080
- Payload has Insufficient Filename Validation in Client-Upload Signed-URL Endpoints - @payloadcms/storage-azure - CVE-2026-34750
- Saltcorn Server allows logged-in users to delete arbitrary files because of a path traversal vulnerability - CVE-2024-47818
You might also like:


See something that needs correcting? Let us knowUpdated November 04, 2025