Description
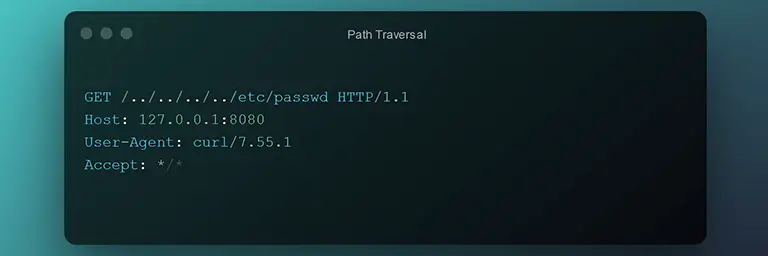
The layout, render, and include tags allow arbitrary file access via absolute paths (either as string literals or through Liquid variables, the latter require dynamicPartials: true, which is the default).
Recommendation
Update the liquidjs package to the latest compatible version. Followings are version details:
- Affected version(s): < 10.25.0
- Patched version(s): 10.25.0
References
Could your website be exposed too?
SmartScanner can check your website for liquidjs has a path traversal fallback vulnerability and gives you actionable findings to investigate.
Start a free scanRelated Issues
- Rollup 4 has Arbitrary File Write via Path Traversal - CVE-2026-27606
- SillyTavern has a Path Traversal issue - CVE-2026-44650
- LiquidJS has an infinite loop vulnerability in its `strip_html` filter - CVE-2026-61556
- jsPDF has Local File Inclusion/Path Traversal vulnerability - CVE-2025-68428
You might also like:
See something that needs correcting? Let us knowUpdated March 12, 2026