Description
Affected versions of datachannel-client resolve relative file paths, resulting in a directory traversal vulnerability. A malicious actor can use this vulnerability to access files outside of the intended directory root, which may result in the disclosure of private files on the vulnerable system.
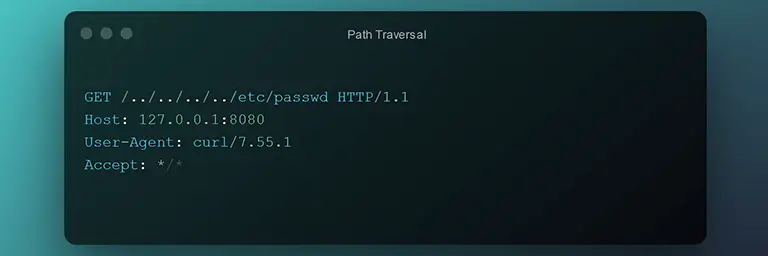
Example request:
Recommendation
No fix is available yet. Followings are affected versions:
- <= 1.0.2
References
Could your website be exposed too?
SmartScanner can check your website for Directory Traversal in datachannel-client and gives you actionable findings to investigate.
Start a free scanRelated Issues
- Directory Traversal in fbr-client - CVE-2017-16217
- Directory Traversal in rtcmulticonnection-client - CVE-2017-16125
- Directory Traversal in cyber-js - CVE-2017-16093
- Directory Traversal in xtalk - CVE-2017-16091
You might also like:


See something that needs correcting? Let us knowUpdated September 14, 2023